Organization Manager
An organization is a tree of units that resources are shared into, and members are given access at a point in that tree. Share a device at a unit and everybody with access to that unit can reach it, including everybody further down.
If you have managed permissions in a file system, you already know the shape. Units are folders, resources are files, and access granted on a folder reaches everything inside it.
| Term | What it is |
|---|---|
| Organization | The whole tree, its members and the resources shared into it |
| Root unit | The top of the tree. Usually renamed to the organization name |
| Subunit | A unit inside another unit |
| Member | A user account belonging to the organization |
| Resource | A device, app, connector, report base, basic credentials set, dashboard, image, geofence or device group |
Any main account can create organizations. A user created inside an organization cannot create organizations of their own.
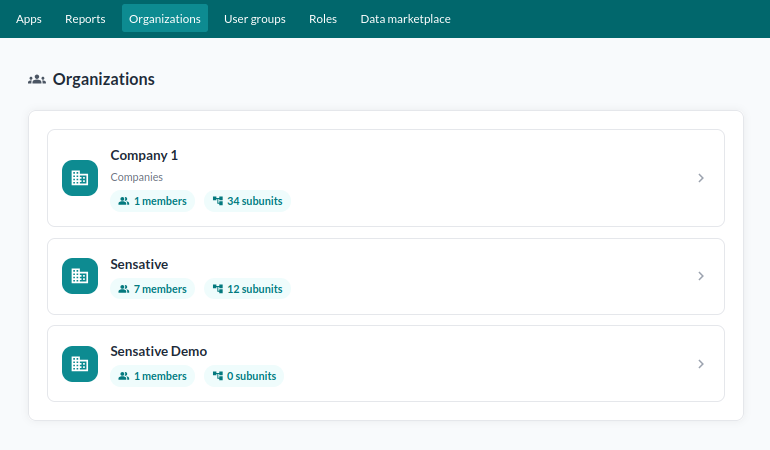
Organizations in the top bar lists every organization you can reach, with its member and subunit counts. Opening one puts you in its tree, with the unit hierarchy in the sidebar.
Start here
Access rights are set on a unit, not on the organization. Manage organization has no permission chips; select a unit in the sidebar tree, and grant the access there.
A first organization, end to end:
- Open Organizations in the top bar and create one. It starts with a single root unit.
- Open the organization and add the people to it, on the Members tab of Manage organization. Adding somebody here makes them a member. It gives them no access to anything yet.
- Click a unit in the sidebar tree. The root unit will do to begin with. Access is granted per unit, so a unit has to be selected before there is anything to grant it on.
- On the unit's Unit members tab, find the person and click the chips for the access they should have: Read, Write, Admin or Peek.
- Put some resources in the unit, from its Resources tab, or by sharing a device to the unit from Device details or Select many.
The member can now reach those resources. Everything after this repeats the same three moves: add a subunit, share resources into it, and grant people access at the level of the tree that matches how much they should see.
Note: a member with no access rights at any unit belongs to the organization but sees nothing. Steps 3 and 4 are what give them access.
How access flows
Two mechanisms, and it helps to keep them apart.
Inheritance. Access granted at a unit applies to that unit and to every subunit below it. Grant a member Read at the root and they read everything in the organization. Grant it three levels down and they read that branch only.
Explicit sharing. A resource is shared into a unit and becomes reachable there. That is done from the unit, or one device at a time from Device details, or many at a time from Select many.
The two combine: a member's access level comes from the units they are granted rights at, and what they can reach comes from what has been shared into those units.
The organization
Manage organization in the top left corner opens the organization itself, whichever unit you are in. It has six tabs.
Summary
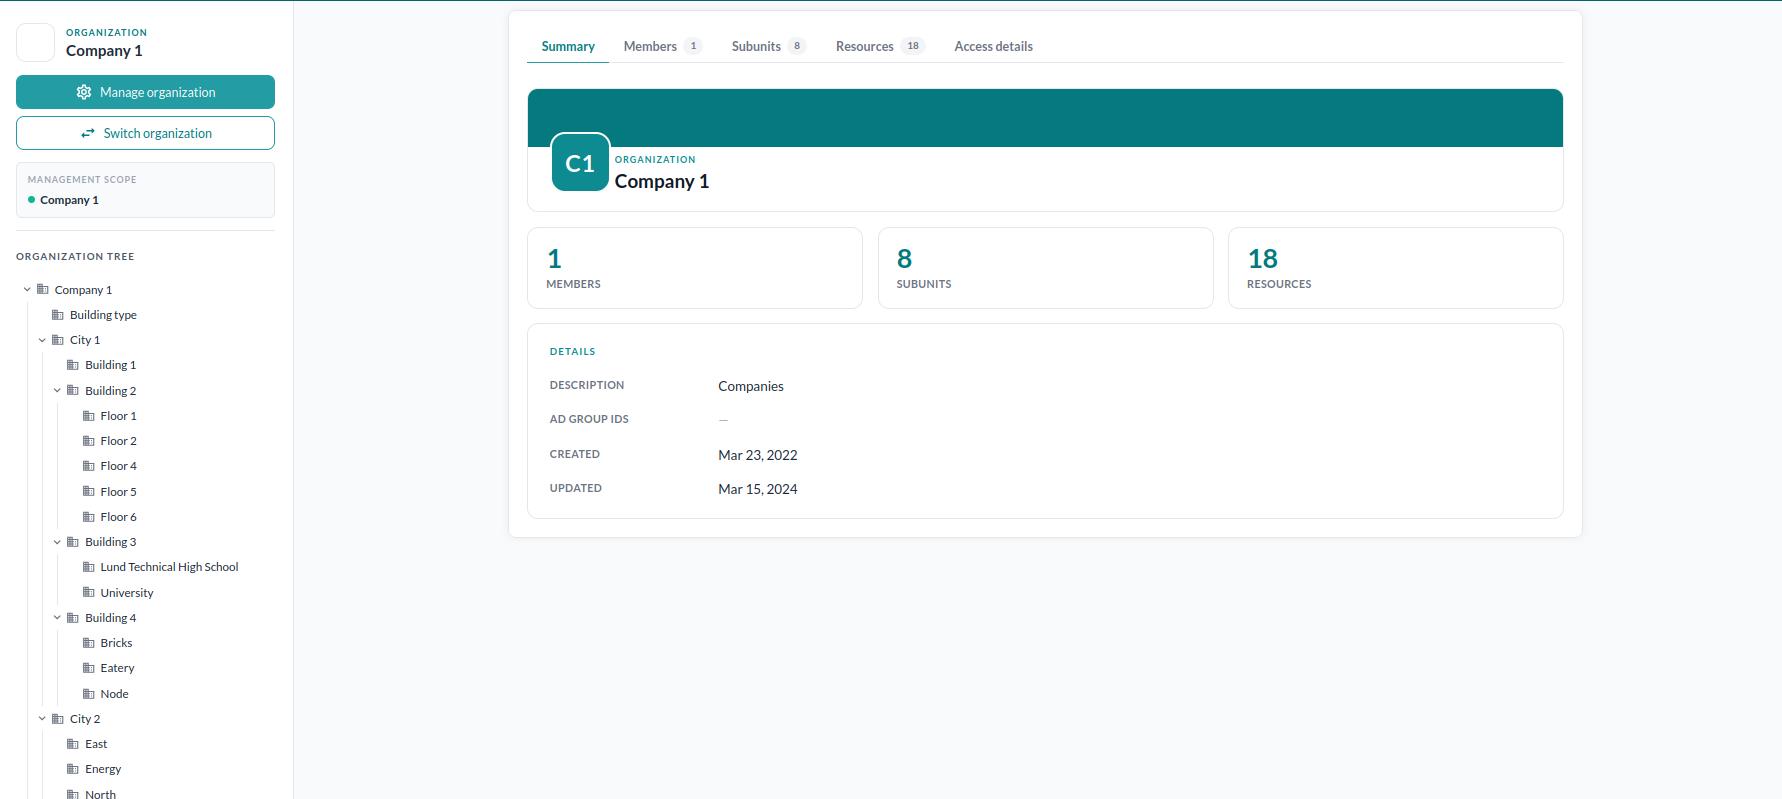
Member, subunit and resource counts, the description, the AD-group mapping, and when the organization was created and last updated.
An organization admin can map the organization to one or more AD groups. AD-group mapping only works where a SAML identity provider is in use. Contact your technical support representative to configure one.
Members
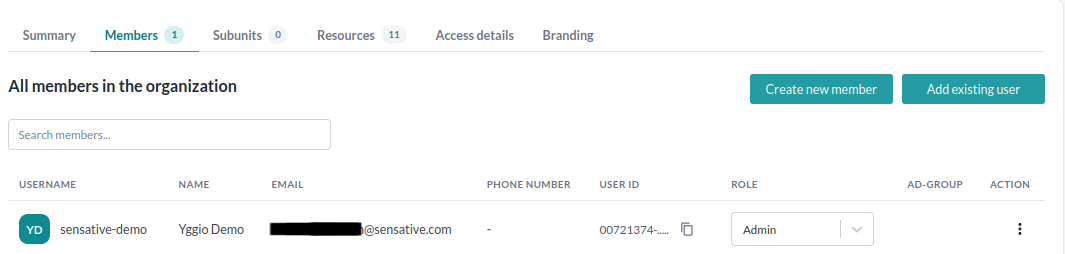
A searchable list of everyone in the organization: username, full name, email, phone number, user id with a copy button, and role. Organization admins and unit managers also see the AD group column, when the organization has an AD group, and the actions for managing each member.
Organization admins and the owner get two ways to add people.
Create new member creates a new Yggio account and puts it in the organization.
| Field | |
|---|---|
| First name, Last name | Required |
| Required. Used for first login and password recovery | |
| Phone number | Optional |
| Username | The login name. Using the email address is common |
| Password | Required. A one-time password is the safer choice |
| Role | The member's platform role |
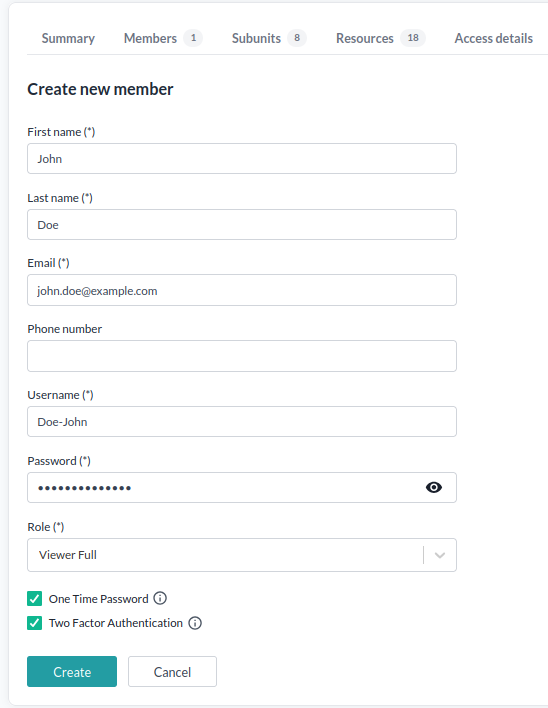
Two-factor authentication is supported and can be switched on here.
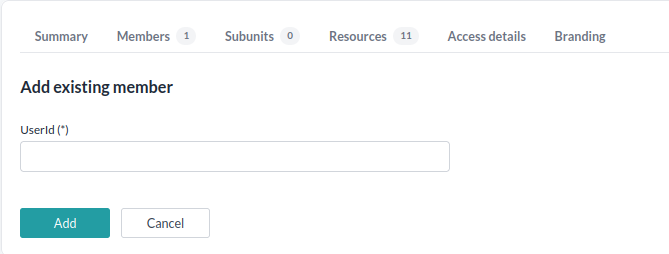
Add existing member adds an account that already exists, so one person can belong to several organizations. Enter the exact username or email address of the user to add.
The owner of an organization can add themselves to it.
Member actions
The menu at the end of a member's row carries:
| Action | Who | What it does |
|---|---|---|
| Edit | Anyone who may see the row | Change the member's name, email, username, password and two-factor setting |
| Disable / Enable | Organization admins and the owner | Blocks the account from logging in, without removing anything |
| Remove | Organization admins and the owner | Takes the member out of the organization. The account itself stays |
| Delete user | Organization admins and the owner | Deletes the Yggio account permanently. It cannot be undone |
Disable, Remove and Delete user are not offered on your own row.
Member roles
Every member's row shows their platform role - admin, editor, installer or one of the viewers. On the rows you may change, it becomes a selector.
Setting a role is not limited to organization admins. If you manage any unit of an organization the member belongs to, you may change or clear their role. Changing a role also requires your own role to be admin.
Nobody changes their own role - unit manager, organization admin and owner alike - so your own row stays plain text. Ask another admin in the organization to change it for you.
Subunits
The organization's direct subunits, with a count and a control to add one. A subunit can be removed from here, which asks for confirmation first.
Resources
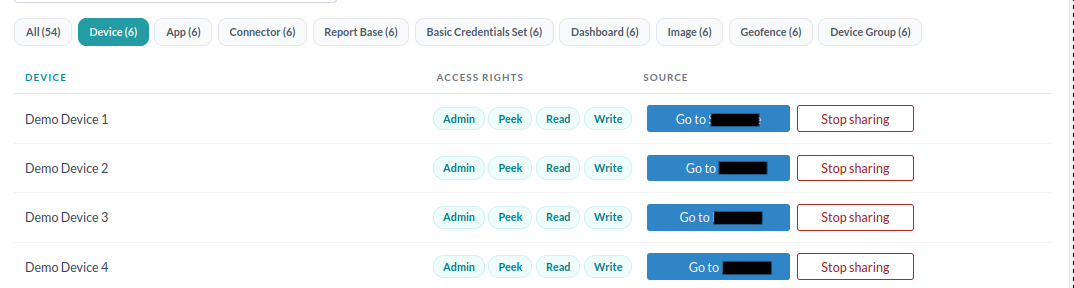
Everything shared into the organization, grouped into tabs by type: device, app, connector, report base, basic credentials set, dashboard, image, geofence and device group.
Each row shows the resource's access rights and a Source column naming the unit it is shared from. From there you can jump to that unit, or stop sharing the resource.
Search filters by resource name across the groups, and the tab counts follow the search. The list pages at 25 rows by default, and the page size goes up to 1000 for an organization with a large fleet.
Access details
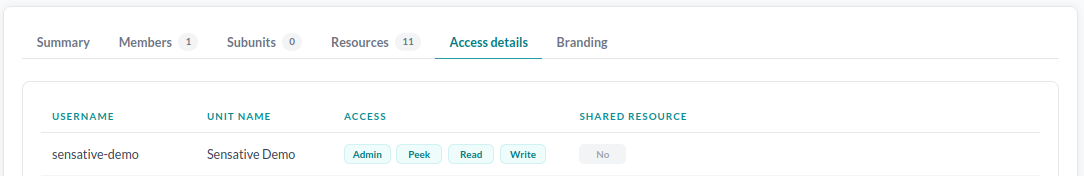
One row per user and unit, showing the rights they hold there and whether their own resources are shared at that unit.
It is the overview that answers "who can reach what", and the fastest way to set a new member up correctly: find somebody doing the same job and match their rows.
The tab is available to organization admins and to anyone who manages a unit.
A unit
Clicking a unit in the hierarchy opens it. A unit behaves like a folder: it holds resources, and access granted here reaches everything below.
The root unit shows the organization's own name and description rather than the literal name "root".
Units have four tabs.
Summary
The unit's name and description, and an icon chosen from a small set - business, groups, people, manage accounts, admin panel settings, assignment, public and account tree. The icon is what tells units apart in the organization lists.
Unit members
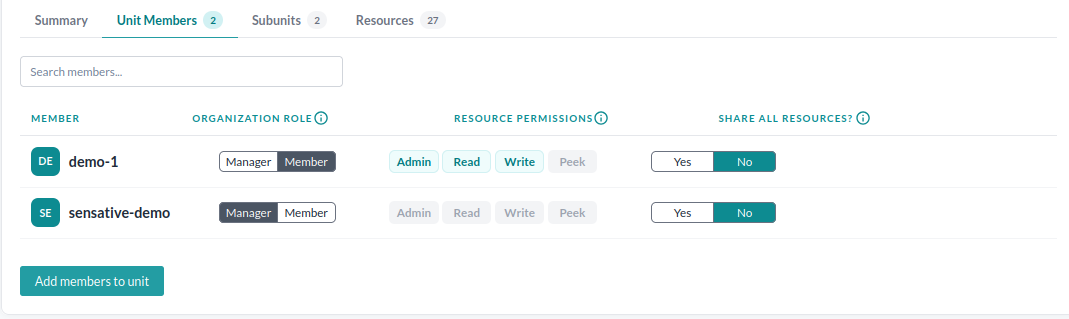
This is where access is actually granted, and it is reached by selecting a unit in the tree first. There is no equivalent on Manage organization: that pane lists who belongs to the organization, while this one decides what they can reach.
Each member of the unit has a row with four things on it.
Organization role is Manager or Member.
| Manager | Manages members and their access rights from this unit down the tree, including setting the platform role of any member other than themselves - as long as their own role is admin. Creating accounts and adding existing accounts to the organization stay with organization admins and the owner |
| Member | The default. No unit management |
Granting and revoking Manager both ask for confirmation.
Resource permissions are four chips. Click one to grant that permission, click it again to revoke it. Each is inherited by every subunit below.
| Admin | Manage the resources at this unit, including setting their access rights and deleting them |
| Read | Read data and see the resources |
| Write | Write data to the resources |
| Peek | The system may read the resources, but they stay invisible to the account holder. Mostly used to give access to connectors |
These are the same four levels as elsewhere in access rights.
Share all resources? is Yes or No. Yes shares everything the member owns at this unit, so everybody with access to the unit - direct or inherited - can work with those devices at their own access level.
A member shares their resources at one unit only. Sharing them at a second unit removes the first. Both directions ask for confirmation, because turning it off revokes everything it granted.
Subunits
The unit's own subunits, where the branch below it is built out.
Resources
The resources available at this unit, whether shared here or inherited. A resource can be unshared from here, which asks for confirmation and names the resource and the unit before it does anything.
Branding
Branding puts your own name, logo and colours on Yggio, so the people you serve see your brand rather than ours. It is worth setting up: for a municipality or a property owner giving tenants access, the platform then looks like part of your own service.
Branding is an add-on. It is not switched on by default. Contact technical support to have it enabled for your organization.
Once enabled, it is set from the Branding tab of the organization, which is available to organization admins and to anyone who manages a unit.
| Tab | |
|---|---|
| Predefined themes | Five ready themes - default, blue, red, purple and grey - previewed before you apply one |
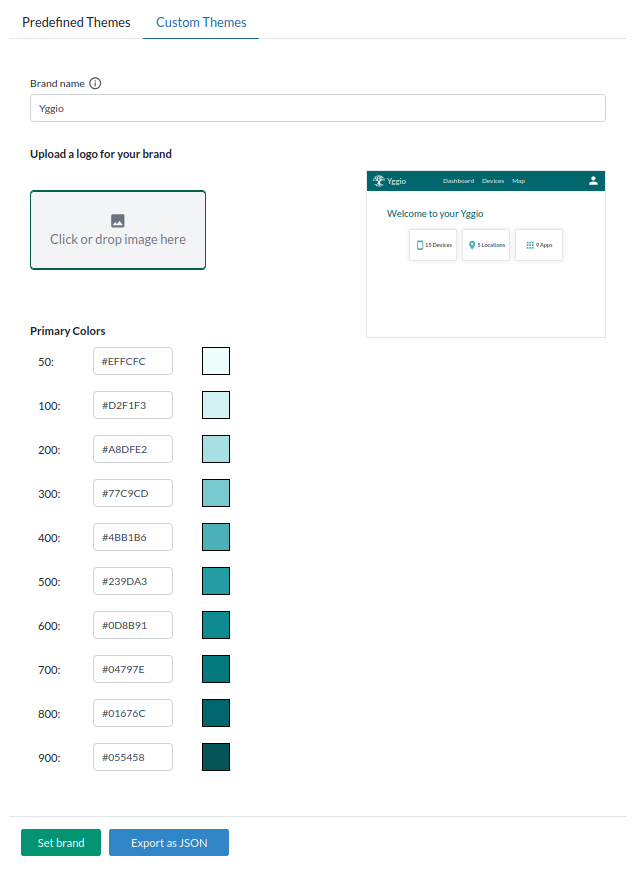
| Custom themes | Your own brand name, logo and primary colours |
The brand name appears in the top left corner of the application, and the logo is shown in the header and on the organization. The predefined themes change the navigation bar:



Custom themes go further: a brand name, an uploaded logo, and the ten shades of your primary colour, with a live preview beside the form. The result can be exported as JSON, which is how the same brand is applied to another organization without setting it again.
Note: a user who belongs to several organizations always sees the default Yggio brand, whichever brand those organizations set.
There is a fuller walkthrough in the training material.